The short version
- Bitcoin Core vulnerability: an AI scan by Project Loupe found a bug that let any connected peer crash Windows, macOS and BSD nodes; Linux nodes were not affected and no coins were at risk.
- The fix shipped in 29.5, 30.4, 31.2 and 32.1 four days after the October 23 report, under a new policy that publishes easily found bugs right away instead of after about a year.
- The crew is watching how many non-Linux nodes update, and three more medium and high bugs fixed in 30.0 that will be disclosed in about two weeks.
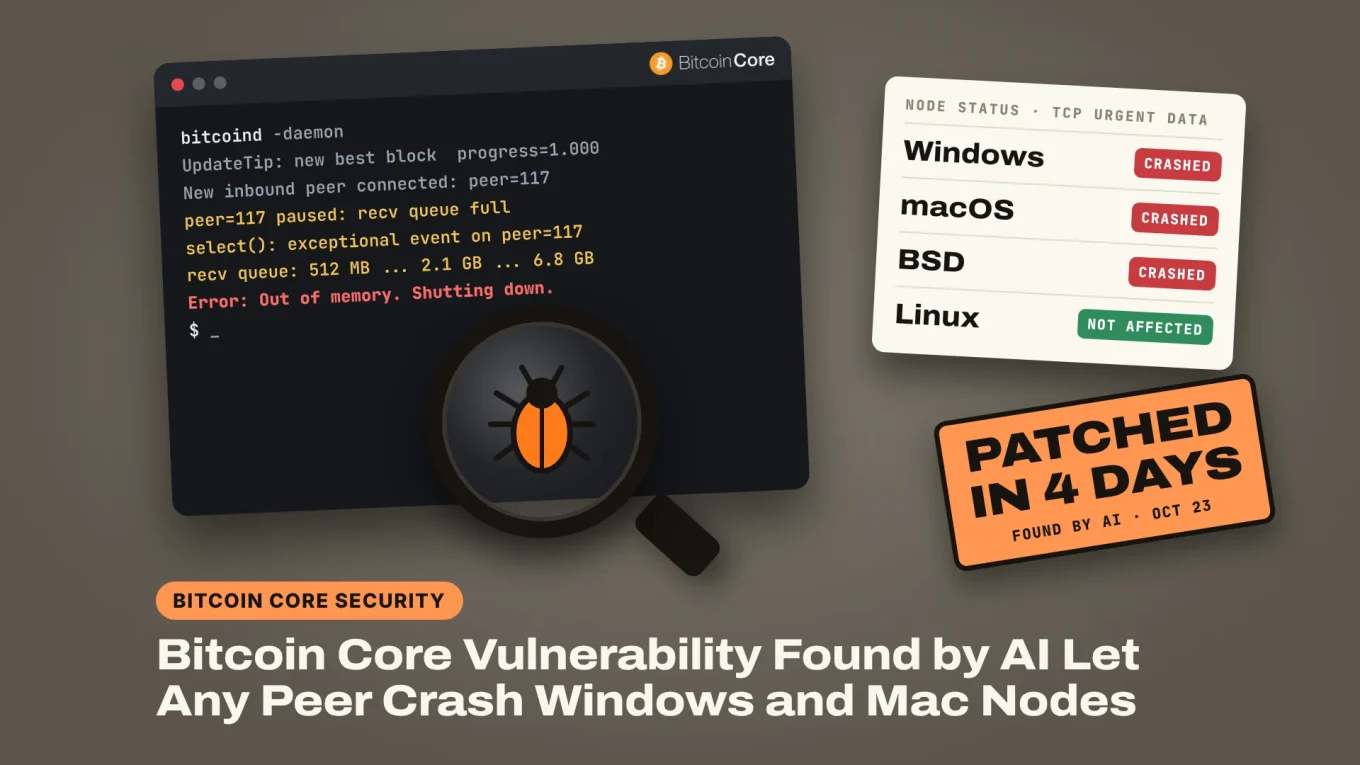
A Bitcoin Core vulnerability found by an AI scanner let any connected peer crash nodes running on Windows, macOS or BSD. Bitcoin Core shipped the fix four days after the report and published the details on October 28, months earlier than it normally would.
It was one of three bugs disclosed at once, all flagged by the same AI tool. None of them lets anyone take coins, and Linux nodes were never exposed to the crash. So why the rush, and do you need to update?
Bitcoin Core maintainer Michael Ford said the bug is why version 32.0 was tagged but never released:

After a drawn out 32.x release cycle, we’ve shipped 32.1. v32.0 was tagged, but not fully announced/released, and after this last-minute discovery: bitcoincore.org/en/2026/10/28/… we decided to ship v32.1, which fixes this bug, along with others (below) and includes other minor
What the Bitcoin Core Vulnerability Did
Bitcoin Core says in its advisory that “a malicious peer can trivially crash any Windows, macOS or BSD node it is connected to.” The trick was TCP urgent data, a rarely used feature of internet connections.
Nodes protect themselves from spam by pausing reads from a peer that sends too much. On systems other than Linux, Bitcoin Core watches its connections with an older method, and that path kept reading urgent data even while a peer was paused. An attacker could keep pushing data until the node ran out of memory and fell over.
The timeline is short. Project Loupe flagged the bug on October 23, developer Gregory Sanders checked it and told the security team the same day, Antoine Poinsot opened the fix on October 26, and versions 31.2 and 32.1 shipped on October 27. Versions 29.5 and 30.4 followed a day later. Bitcoin Core rates it medium severity.
Sponsored · Affiliate link
Save 20% on fees trading on WEEX
Base Camp may earn a commission if you sign up. It never affects what we write.
Two More Bugs From the Same AI Scan
The second advisory covers a Bitcoin Core bug that is a slower version of the same problem. A peer that pretends to be very old software could make a node’s memory grow by up to 2MB an hour per incoming connection and 5MB an hour per outgoing one.
The third is rated low and is close to impossible to use. A miner would need to mine several thousand blocks of unusual transactions, about a month of the whole network’s output, to make some nodes shut down later. Nodes on 32-bit systems or FAT32 drives are still affected even after the update.
Loupe is a free scanner from Spiral, the Bitcoin team funded by Block. It runs AI agents over open-source code and makes each one write a test that proves its finding before anything gets reported. That cuts the junk reports that usually come with AI bug hunting.
SIDE TRAIL: Crypto Hacks Fell to $129M in October, and DeFi Had Its Quietest Month of 2026
Why Bitcoin Core Stopped Waiting a Year
Normally, Bitcoin Core keeps medium and high bugs quiet until the last affected version reaches end of life, roughly a year after the fix ships. That gives slow upgraders time to catch up.
On October 22, six days before these advisories, Poinsot told the developer mailing list that this no longer works for some bugs. The project has seen “an increase in the number of reports for security vulnerabilities that can be easily (re-)discovered,” he wrote, “largely due to LLMs drastically reducing the bar to find certain classes of issues.”
So bugs flagged as “easily discoverable” now get a fixed release for every maintained version as fast as possible, with the advisory out the same day. In other words, if a chatbot can find it, so can an attacker, and hiding it only delays the patch.
The three bugs prove the point. Developer L0rinc found the memory bug independently, six days after Loupe did. The undo-file bug was reported three separate times, the last on October 23.
Who Needs to Update?
Anyone running Bitcoin Core on Windows, a Mac or BSD should install the Bitcoin Core update now: 29.5, 30.4, 31.2 or 32.1. Node boxes such as Umbrel and Start9 run on Linux, so the crash bug never reached them, but the other two bugs touch every system.
Version 29.5 is the last of the 29 line, which is now end of life. Three more medium and high bugs, fixed back in 30.0, will be disclosed under the old rules in about two weeks.
Bitcoin barely noticed. It trades at $79,843 at the time of writing, down 1.5% in 24 hours and below its 50-day moving average at $81,976, a slide that has more to do with the Fed than with node software.
TRAIL MAP: What Is Crypto, Really? Bitcoin and Blockchains in Plain English
The bigger story behind this Bitcoin Core vulnerability is the speed. Four days from an AI report to a patched release is fast for a project this careful, and it sets the pace for the next round. More of these advisories are coming.
In crypto since 2016. Trades the macro picture and reads the market on the high timeframes.
More from TheCryptoMonk →