The short version
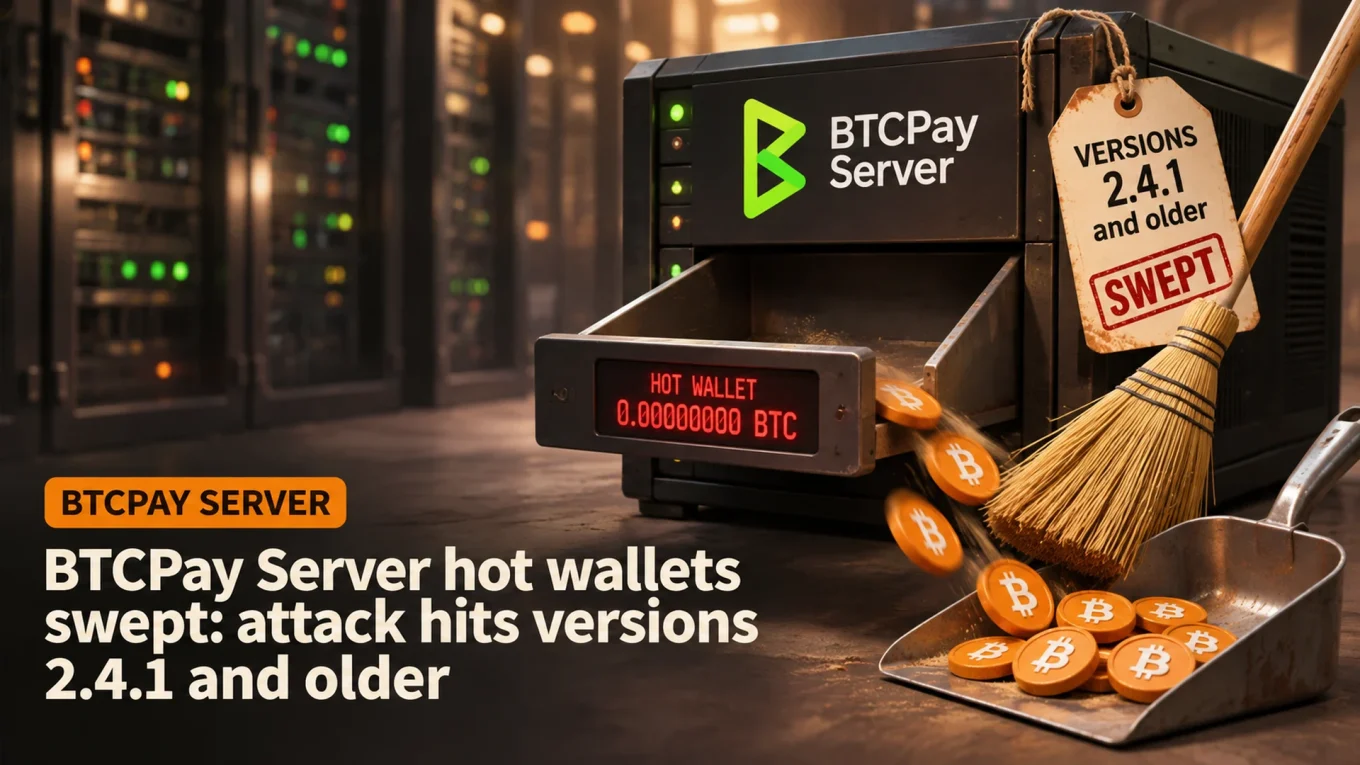
- BTCPay Server hot wallets were swept overnight after attackers logged in as admin on instances running version 2.4.1 or older; no loss figure yet.
- There are no credible reports of drains on the latest 2.4.7, so the fix is to update or keep the server off, and to move funds out of any hot wallet on an old version.
- Next: BTCPay’s blog post with the full details of how the attackers got in. Follow Base Camp on X to see it when it lands.
BTCPay Server, the free, self-hosted tool many merchants use to take Bitcoin payments, told every operator to switch their servers off on Sunday night. At 22:25 UTC the team said it was getting reports of hot wallets on BTCPay instances “being swept by unauthorized attackers.”
Six hours later it had found the way in. The attack works on old versions, and the latest one looks safe:

📢 Our incident response investigation identified an attack vector targeting instances running versions 2.4.1 (Jul 23, 2026) or older.
We have no credible reports of hot wallet drains for users running the latest 2.4.7 release. We again urge everyone to keep their BTCPay Server
What Happened to the BTCPay Server Hot Wallets?
Attackers logged in to older BTCPay Server instances as admin and emptied the hot wallets on them. Lead developer Nicolas Dorier wrote at 00:28 UTC that the reports all came from servers older than 2.4.2 and that “the attacker managed to log in as admin on those instance, we are still trying to figure out how.” BTCPay’s own public servers, on 2.4.7, were not hit.
A hot wallet is the one whose keys sit on the server itself, so the server can send coins without a person signing. Handy for refunds and payouts. Also the first thing an attacker with admin access goes for. Watch-only wallets, where the keys stay on the merchant’s own device, have no keys on the server to take.
No one has given a figure for how much was taken or how many servers were hit.
Sponsored · Affiliate link
Save 20% on fees trading on WEEX
Base Camp may earn a commission if you sign up. It never affects what we write.
Which BTCPay Server Versions Are Affected?
Version 2.4.1, released on July 23, and everything older. BTCPay says it has “no credible reports” of drains on 2.4.7, the latest release, and Dorier added that anyone who has updated at least once since 2.4.2 came out in August has “no reason to panic.”
In other words, the servers being swept are the ones nobody has updated for more than three months. Hosting companies are cleaning up for their customers: BTCPay thanked LunaNode and other hosts for shutting down instances still on the old versions.
The Second BTCPay Server Hack Since August
This is the second time in three months. On August 7, BTCPay pushed version 2.4.2 to fix a flaw that let an attacker take the credentials for a merchant’s LND Lightning node, and attackers used it to drain Lightning nodes in the days after. That time BTCPay’s on-chain hot wallets were not affected. This time they are the target.
BTCPay has shipped security releases ever since. Version 2.4.7 came out on October 29 as an emergency update fixing one critical and several medium-severity bugs found by Anthropic’s AI security scanner.
SIDE TRAIL: Keystone Wallet Breach: Maker to Destroy 18,835 Devices After Key Theft
What Should BTCPay Users Do Now?
Update to BTCPay Server 2.4.7, or keep the server off until you can. On a server that ran 2.4.1 or older, treat the hot wallet’s seed as exposed: move whatever is left to a new wallet whose keys never touched that server. BTCPay’s other advice is simple: “don’t keep too much in your Hot Wallet.”
If you were hit, BTCPay asks for details and logs at [email protected]. Dorier said a blog post with the full details is coming.
TRAIL MAP: Your First Crypto Wallet, Set Up Safely: Hot vs Cold and the Seed Phrase
VikingXBT has been trading crypto since 2017. The focus is futures, onchain data and automation. Onchain flows get checked before a chart is trusted, and anything repetitive gets automated. VikingXBT built Base Camp's own onchain scanner, which flags bundlers, snipers, dev holdings and wallet clusters in one view, and backtests strategies before trading them.
More from VikingXBT