Correction, November 16, 2026: an earlier version called this a suspected Lighter exploit and said Lighter had made no statement. Lighter has since said the incident involves a single compromised external party, not its protocol, and has paused withdrawals. Traders trace it to leaked API keys of two market-maker accounts.
The short version
- The Lighter exploit was not a hack of Lighter itself: Lighter says the $10.39 million USDC withdrawal on November 16 involved a single compromised external party.
- Traders on X say leaked API keys let an attacker drain two market-maker accounts, about $15.5 million in total; Lighter has not confirmed that or the total.
- Lighter has paused all withdrawals and pool creation; LIT is down 11.8% in 24 hours at $2.66, and the contract still holds about $513 million in USDC.
The Lighter exploit that pulled $10,393,056 in USDC out of the perp DEX’s Ethereum contract on Monday, November 16, was not a hack of Lighter itself. Lighter says it “appears to involve a single compromised external party.” Traders tracing the money say leaked API keys of two big market-maker accounts let an attacker empty them.
The withdrawal landed at 10:11 UTC. Security firm Hacken flagged it as a suspected exploit half an hour later. Lighter answered at 11:02 UTC:

We are actively investigating a security incident that appears to involve a single compromised external party.
As a precaution, we have temporarily suspended all withdrawals and pool creation while we investigate the circumstances and assess the full impact.
What Happened at Lighter?
A wallet first used that morning claimed $10.39 million from Lighter’s main contract through withdrawPendingBalance, the normal call traders use to take money out.
Lighter is a layer-2 exchange for perpetual futures. Traders deposit USDC on Ethereum, trade on Lighter’s own chain, and withdraw back to Ethereum. The contract paid out because, as far as it could tell, the request was valid.
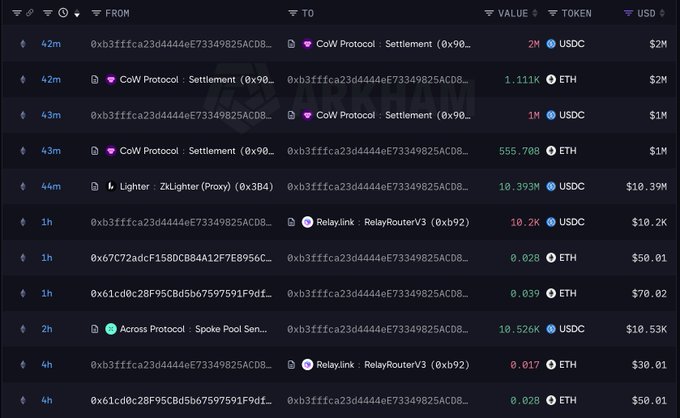
The wallet swapped the USDC for about 5,750 ETH through CoW Protocol within minutes. By 11:14 UTC it had sent five 160 ETH pieces to new addresses and still held about 4,805 ETH, roughly $8.7 million.
Lookonchain says the attacker is now also moving money into Hyperliquid to buy XMR, the privacy coin:

According to @0xTria, API keys belonging to two market makers on @Lighter_xyz were leaked, resulting in ~$15.5M being stolen!
The attacker is now depositing the stolen funds into #Hyperliquid to buy $XMR.
arkm.com/explorer/addre…
Sponsored · Affiliate link
Save 10% on fees trading on FOMO
Base Camp may earn a commission if you sign up. It never affects what we write.
How Leaked API Keys Drained Two Accounts
The breakdown going around X comes from Korean traders, shared by analyst 0xTria:

korean friends breakdown on lighter, if it's right this wasn't a protocol hack, it's leaked api keys of 2 big mm accounts
attacker closed the victims' positions, created a 0% fee public pool from the victim account, put in ~$10k to own 99.99% of it, then moved the victim's usdc
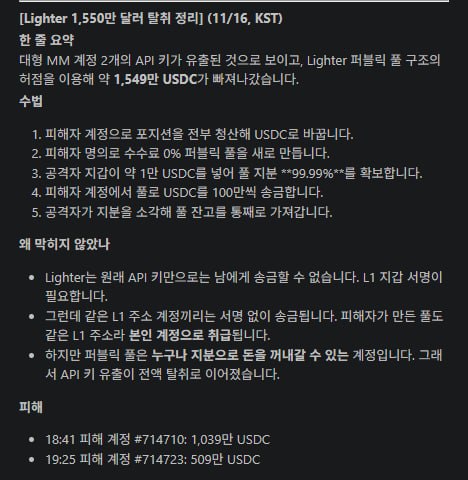
An API key lets a trading bot place and close orders. On Lighter it can’t send money to another user. The attacker got around that in four steps:
- Closed the victims’ open positions.
- Created a public pool with 0% fees from a victim’s own account.
- Put in about $10,000 to own 99.99% of that pool.
- Moved the victim’s USDC into the pool in $1 million batches, then redeemed the pool shares.
That worked because moves between accounts under the same Ethereum address need no signature, and a pool the victim creates counts as the victim’s own account. In that version, two accounts were hit: about $10.39 million from #714710 and $5.09 million from #714723, about $15.5 million in total.
Lighter has not confirmed the API-key route or the total. Its statement points the same way, though: the Lighter exploit hit one outside party, not the exchange’s code.
Can You Still Withdraw From Lighter?
No. Lighter withdrawals are off for now: the exchange has temporarily suspended all withdrawals and pool creation “while we investigate the circumstances and assess the full impact.” It has given no restart time.
The pot is still there. The Lighter contract holds about $513 million in USDC, and the $10.39 million is about 1.4% of the $743 million DefiLlama counts in Lighter across its chains.
Running a trading bot? Check your Lighter API keys: revoke every one you don’t use, and replace the ones you keep. Ignore “refund” links and DMs that show up after an incident like this. Those are the next exploit.
SIDE TRAIL: Lighter CFTC Plan Sent LIT Up 12% in 40 Minutes. Two Days Later, the Pump Was Gone
LIT Price After the Lighter Exploit
The LIT price is $2.66 at the time of writing (11:17 UTC), down 11.8% in 24 hours on CoinGecko, after a dip of more than 17% at the worst point. Its market cap is about $665 million.
What LIT needs next is withdrawals switched back on and a final number from Lighter.
TRAIL MAP: Biggest Crypto Hacks in History, Ranked: Binance’s $6.3B Breach Takes No. 1
TheCryptoMonk has been trading since 2017 and reads the market from the top down. The focus is macro and the high timeframes: where stocks, rates and liquidity are heading, and what the weekly and monthly charts say about Bitcoin. Short-term noise matters less than the bigger trend.
More from TheCryptoMonk