The short version
- Trezor data breach: shipping partner Skladon says an attacker exported names, phone numbers, emails and home addresses from about 27,000 orders placed August 9 to November 7.
- No wallet backups, PINs or passphrases were involved, but Trezor warns of scam calls and physical risk, since the leak shows who bought a hardware wallet and where they live.
- It is Trezor’s third partner incident since August, after ShipMonk (80,689 customers) and Brevo (347,149 email contacts).
A hardware wallet keeps your coins offline. The box it arrives in is another matter. In the latest Trezor data breach, the company says an attacker got into the systems of its shipping partner Skladon and exported customer details from about 27,000 orders.
The orders were placed between August 9 and November 7. Full names, phone numbers, email addresses and delivery addresses were all in the export, along with what each customer bought and what they paid. Trezor posted the warning at 16:18 UTC on Monday, November 16, a day after Skladon told it about the break-in:

Data breach involving Skladon
On 15 November, Skladon, one of our delivery partners, notified us that an attacker had gained unauthorized access to Trezor order data it holds. We’re still investigating with Skladon, but we want to let you know now.
What we know:
• We believe
What Did the Trezor Data Breach Expose?
Contact details and order history, but nothing that can open a wallet. According to Trezor’s notice, the attacker got in on November 7 and took:
- Who you are: full name, phone number and email address.
- Where you live: the delivery address on the order.
- What you bought: order date, product name and price.
Wallet backups, PINs and passphrases were not involved. Trezor says neither it nor Skladon ever holds them, and that its own systems were not compromised. Your seed phrase is still yours alone.
Trezor emailed every affected customer it can still reach. A small number who ordered between August 9 and 14 may also be in the leak but can’t get that email, because their details had already been anonymized under Trezor’s 90-day policy. Customers who ordered after November 7 are not affected. Skladon delivers to many countries, so the leak isn’t limited to one region.
Sponsored · Affiliate link
Save 20% on fees trading on WEEX
Base Camp may earn a commission if you sign up. It never affects what we write.
Why Is Trezor Warning About Physical Risk?
Because the leak tells criminals who bought a hardware wallet and where that person lives. Trezor tells customers to be careful about who knows they own crypto, and to call local police first if a message turns threatening. Security firm Exploitex put the same point in two lines:

Trezor reports a breach at shipping partner Skladon involving ~27,000 orders. Wallet backups weren’t involved, but exposed addresses and purchase details raise phishing and physical-security risks.
Never share your backup.
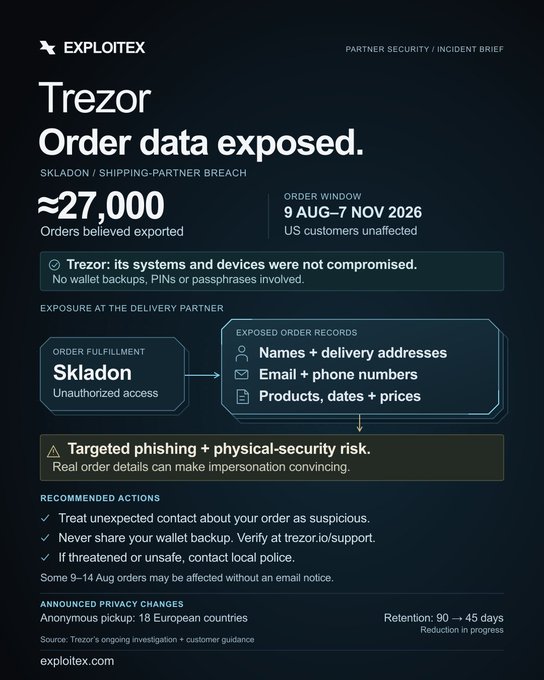
The more likely problem is phishing. Scammers can now quote a real order, down to the product and the price, and they can reach buyers by phone or even by letter. Trezor says some customers have already reported scam calls. Its line on that is simple: “Nobody from Trezor will ever cold-call you or ask for your wallet backup.”
So treat any unexpected message about your order as suspicious. Skip the links, QR codes and phone numbers inside it and go to trezor.io/support yourself.
SIDE TRAIL: Gnosis Pay Data Breach Leaks Home and Wallet Addresses
Third Partner Incident in Three Months
This is the third Trezor customer data breach that started at a partner since August, and Trezor admits the pattern itself. “We know this is not the first time customer contact details and addresses have been exposed in an incident involving one of our partners,” the notice says.
The run so far:
- August 13: Trezor said its shipping provider ShipMonk had suffered unauthorized access. The first count was 11,742 customers with full contact details and 1,947 with partial ones.
- September 4: ShipMonk said the breach was bigger. Old US order data from 2019 to 2021, which Trezor had been told was deleted, added about 67,000 more customers, for a total of 80,689.
- September 9: Attackers abused email platform Brevo to send Trezor newsletter readers a fake “Critical Security Alert” that asked for their wallet backup. Brevo confirmed that 347,149 contacts were exported, and about 2,500 people clicked before the site came down.
- November 16: Skladon, about 27,000 orders.
Three different vendors, one repeat problem: the weak point keeps sitting outside Trezor’s own systems, with whoever handles the boxes and the mailing list. Bitcoin security author Luke de Wolf drew the practical lesson for buyers:

Another unfortunate third-party breach at Trezor. These things are happening more and more frequently, and sometimes there's only so much that due diligence can protect any company.
That's means: avoid using your primary email, phone number, and especially address when ordering
What Is Trezor Changing After the Skladon Breach?
Less data, kept for less time. From November 16, customers in 18 European countries can order with anonymous pickup at a parcel locker or pickup point, so their name and home address never reach Trezor. The company says it is working on the same option for the US.
Trezor is also cutting how long it keeps order data from 90 days to 45, and says it wants to go lower. It is reviewing its third-party partners and the security rules it sets for them, and it has informed the data protection authority.
For scale, this Trezor data breach reached back about three months of orders, almost exactly the 90 days the company keeps them today.
TRAIL MAP: 10 Common Crypto Scams and How to Spot Them
TANG has been trading crypto since 2017. The focus is technicals, DeFi and onchain data. On the chart, that means high-timeframe support, moving averages and momentum divergences. Onchain, it means regular checkups on where the data puts the cycle. TANG once ran CryptoJungle, a free community for researching and trading together, and brings that same spirit to Base Camp as one of its co-founders.
More from TANG