The short version
- Optimizely malware ran on Ledger’s website and 177 other organizations’ sites on November 16, swapping Bitcoin, Ethereum, Solana and five other kinds of crypto addresses for the attacker’s.
- Report URI counted about $7,040 in the attacker’s wallets by 19:25 UTC; the same script also skimmed cards and loaded iPhone exploit kits.
- Optimizely says it fixed the flaw and removed the code; if you sent crypto on November 16, check that the receiving address is really yours.
On Monday, November 16, the website of Ledger, the hardware wallet maker, served code that could swap a crypto address for an attacker’s. The Optimizely malware came through a tool that 178 organizations trusted to load on their own pages, and it reached names as big as Zoom and HSBC.
Security researcher Scott Helme of Report URI found the code and published the full breakdown that evening. The mass clean-up started around 20:40 UTC, more than 16 hours after the first infected script appeared. The open question for anyone who sent crypto that day is simple: did the address you pasted belong to you?
Helme summed it up on X:

This is a big one.
We found malicious JavaScript being served through Optimizely to some of the world's largest websites.
178 organisations affected, with everything from crypto theft and card skimming to iOS exploits.
Zoom, BBC, CNN, HSBC, Salesforce, GitLab, KLM, IKEA,
How Did Optimizely Malware Get Onto Ledger’s Website?
Through Optimizely, not through Ledger itself. Optimizely Web is an A/B testing service: a site loads one script from cdn.optimizely.com, and that script runs on every page. Each customer can add its own “Project JavaScript” to it.
The attacker wrote code into that field across customer projects. The file still came from Optimizely’s own servers, so browsers and most site defenses treated it as normal. Report URI checked 1,611 Optimizely scripts and found 188 infected, belonging to 178 organizations. The first one showed up at 04:21 UTC (11:21 p.m. Sunday in New York), and Optimizely’s own website was on the list too.
Optimizely posted a notice on its status page at 01:02 UTC on Tuesday. It said an attacker “exploited a vulnerability in Experimentation” to add the code, and that it has “fixed the vulnerability and removed the injected code from affected projects.” It has not said publicly what the flaw was.
Sponsored · Affiliate link
Save 20% on fees trading on WEEX
Base Camp may earn a commission if you sign up. It never affects what we write.
What the Script Did to Crypto Addresses
It replaced valid Bitcoin, Ethereum and other EVM, TRON, Solana, TON, Litecoin, Bitcoin Cash and Dogecoin addresses with the attacker’s, everywhere it could reach. That meant the page itself and your clipboard, down to the iOS share sheet. Copy an address from any page while an infected tab was open, and you could paste the attacker’s.
That was only one payload. The script also skimmed card numbers typed into a site’s own forms, sent cookies and screenshots to the attacker, and loaded iPhone exploit kits, including DarkSword on iOS 18. Crypto and trading names on the list include Ledger, IG, OANDA and its Coinpass exchange, interactive investor, TMS Brokers and Betashares. Ledger’s script was cleaned at 20:41 UTC.
So how much did it take? Less than you might fear. Report URI counted about $7,040 in the attacker’s wallets by 19:25 UTC, after the attacker had already swept coins to exchanges at 13:03 UTC:
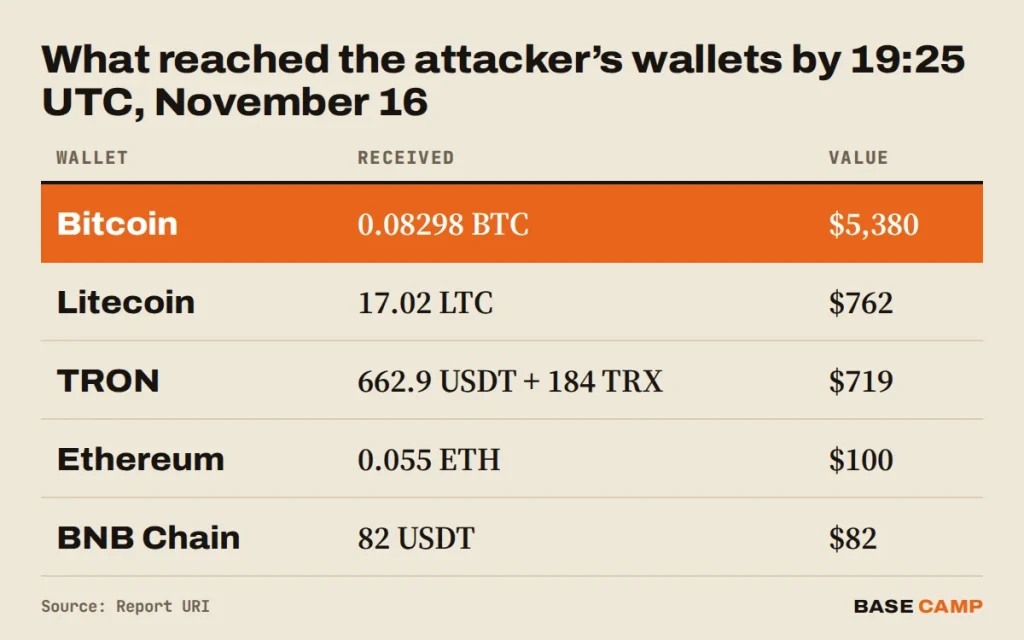
In other words, the Optimizely malware ran on some of the busiest sites on the internet and, by that count, collected less than a decent day of trading.
SIDE TRAIL: DarkSword iOS Exploit Targets Crypto Wallets: Check Your iPhone Version
Did You Copy a Poisoned Address?
Check every transfer you made on November 16. If the address the money went to doesn’t match the one you meant to use, the swap may have hit you, and an onchain transfer can’t be reversed.
The chain of events is worth spelling out:
- The trigger: an open tab on one of the 178 sites, even one with nothing to do with crypto, such as a news page.
- The swap: the script rewrites the address on the page or in your clipboard.
- The damage: you paste, check the first few characters, and send to the attacker.
A hardware wallet helps only if you read the full address on the device’s own screen before you confirm. The website can lie; the device screen can’t be reached by this script. Report URI also tells iPhone users to update to iOS 18.7.3 or later, or iOS 26.3 or later. Paid by card on one of the sites that day? Watch your statements.
TRAIL MAP: How to Send Crypto Without Losing It: Networks, Addresses and Test Transactions
This is not Ledger’s first brush with code from someone else’s pipeline. In December 2023 an attacker pushed a poisoned version of Ledger’s Connect Kit library to the apps that used it. This time the bad code wasn’t even Ledger’s, which is exactly the point Helme makes in his write-up: “trusted JavaScript doesn’t always remain trustworthy.”
Teddy has been trading crypto since 2016. The focus is altcoins and EMA setups: finding coins sitting on key levels, waiting for support to hold or a range to be reclaimed, and trading the move from there. Bitcoin sets the tone, but the opportunities are usually in the alts.
More from Teddy